
New Delhi: The Bharatiya Janata Party has criticised Congress leader Rahul Gandhi over alleged security vulnerabilities involving personal information submitted by students through the “Chhatron Ki Goonj” campaign website.
BJP leader Amit Bhandari accused Gandhi of “playing with the present and future of students”, questioning the safeguards in place for personal details collected through the registration process. He also asked whether Gandhi would take responsibility if students became targets of cybercriminals.
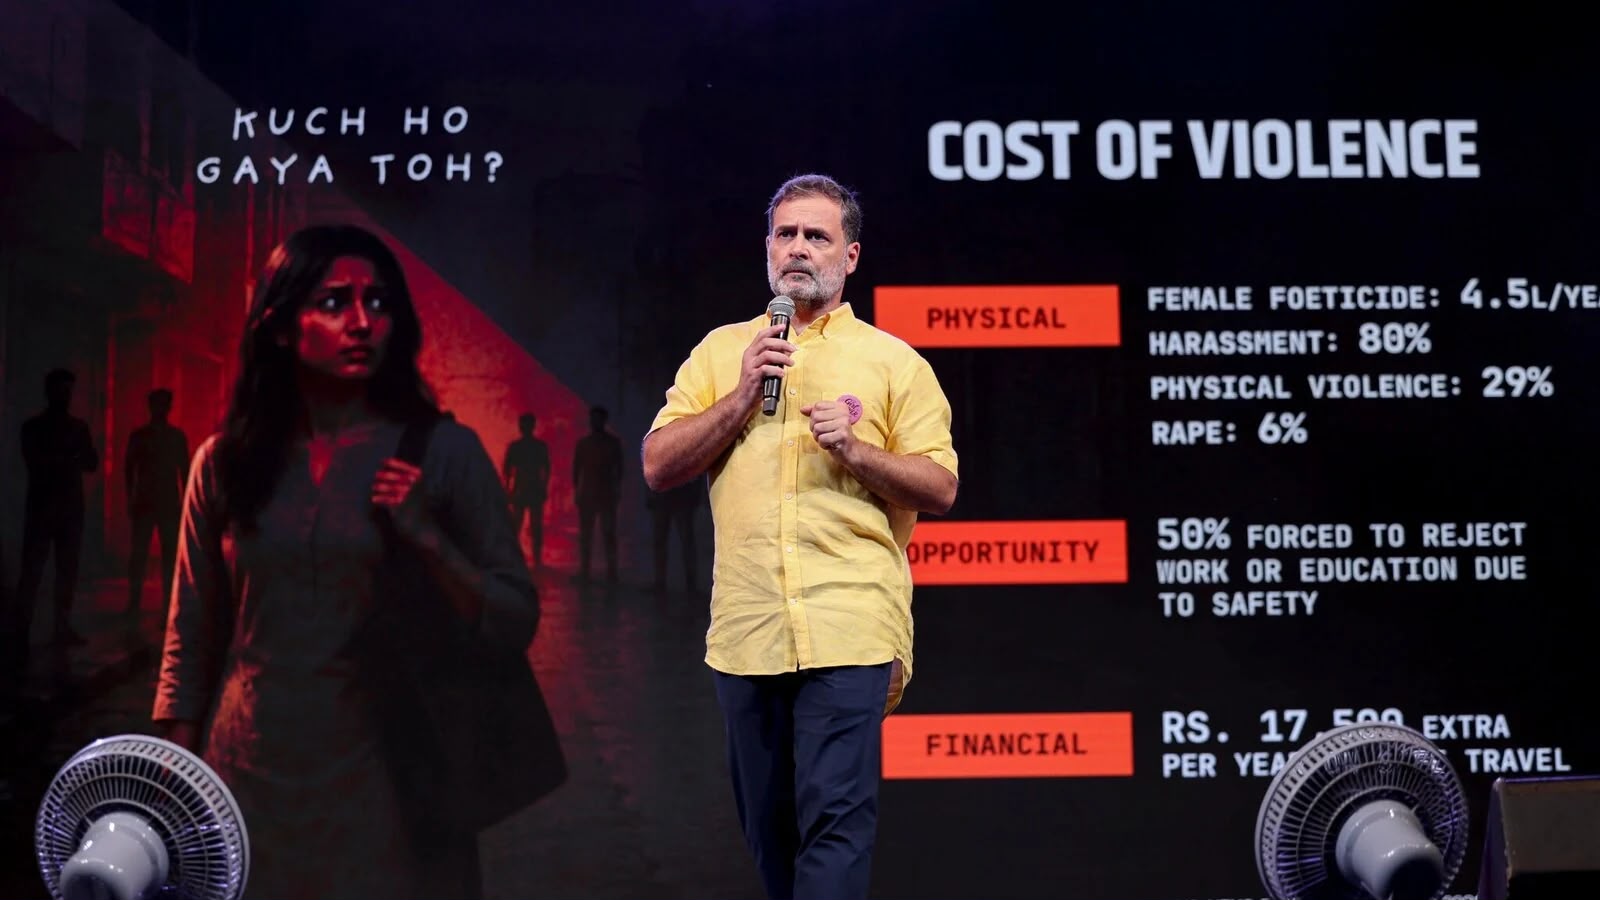
The “Chhatron Ki Goonj” campaign was launched by Gandhi in June to raise issues including examination paper leaks, education costs, employment opportunities and problems faced by students. The campaign’s official website currently invites students to join the movement and register for events, including the Indore programme held on September 19. (Rahul Gandhi)
A report published on September 20 alleged that registration information on Gandhi’s website had been exposed because of cybersecurity vulnerabilities. According to security researcher Shashi, potentially 1,56,439 records could be accessed when he examined the website. The report alleged that retrieving registration records did not require an account, password, cookie, token or API key. (OpIndia)
The researcher also alleged vulnerabilities on other Congress-linked platforms, including the Mahila Congress website. These reportedly involved access to certain user information and other data without conventional login protection. The claims have not been independently established through a public technical audit.
According to the report, the researcher said he alerted Congress functionaries about the vulnerabilities before approaching CERT-In, the Indian Computer Emergency Response Team. He later said members of the Congress technology team contacted him and that several pages collecting information and donations were subsequently disabled.
The researcher said Congress later informed him that the reported issues had been fixed, although he claimed he had not received formal confirmation from CERT-In regarding closure of the matter. (OpIndia)
The controversy has now added a cybersecurity dimension to the wider political debate surrounding the “Chhatron Ki Goonj” campaign, which has been holding student-focused programmes across several cities.